ARTICLES
Intelligence for teams defending what's outside the firewall
Research, breakdowns, and practical guidance.
How Account Takeover Attacks Work
Account takeover (ATO) attacks often start with access that looks legitimate. An attacker uses a stolen password, a leaked session token, a phishing link, or a fake login page to get into a real account. Once inside, the
May 8, 2026 · 7 min read
What Is Credential Stuffing?
Credential stuffing is when attackers use stolen usernames and passwords to break into accounts. They do not guess passwords. They use login details that have already leaked from past breaches, then test them across webs
May 2, 2026 · 7 min read
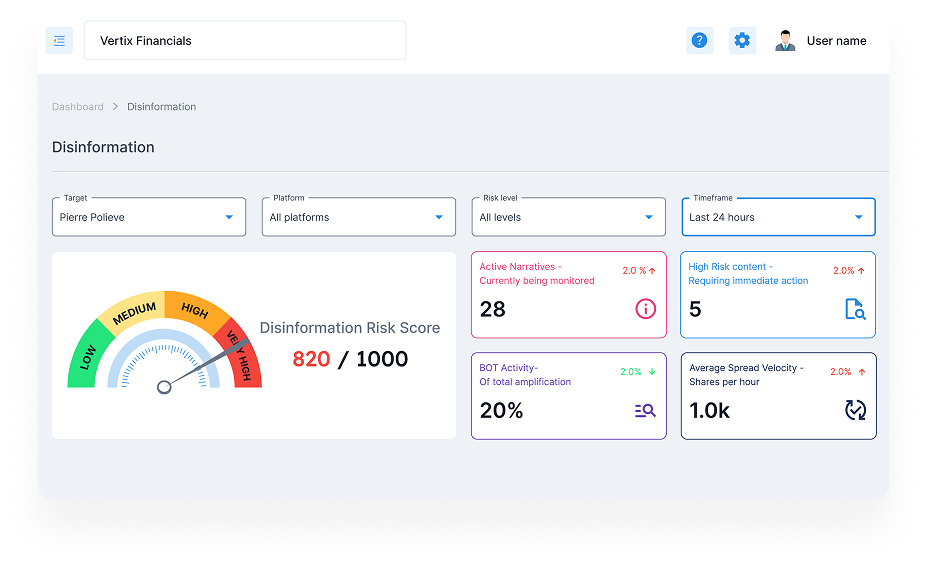
Introducing Disinformation Security
Disinformation is the new frontier of cyber threats. It leverages false narratives, fake accounts, and coordinated postings to drive fraud, manipulate perceptions, and drain organizational resources. That’s why Styx Inte
Feb 18, 2026 · 5 min read
Actionable Intelligence: Why Context Beats Raw findings
Why Raw Alerts Slow Down Teams If you work in security, you already know the problem: you don’t need more alerts. You need to know what matters, why it matters, and what to do next. That’s what people mean by actionable
Feb 13, 2026 · 6 min read
Styx Intelligence is Now Available on AWS Marketplace
We’re excited to share that Styx Intelligence is now available on AWS Marketplace. This is great news because AWS Marketplace is one of the most trusted places organizations go to discover and adopt cloud software. Being
Feb 10, 2026 · 3 min read
How Stolen Credentials Became the Easiest Way Into Your Company
Today, many serious incidents begin with something simple: someone using a valid username and password (stolen credentials) that was exposed outside the company. Where does that exposure happen? In practice, it comes fro
Jan 27, 2026 · 7 min read
Why Cybersecurity Teams Need a Proactive Approach… Not a Reactive One
A proactive approach is the difference between stopping risk early and cleaning up damage later. Most security teams still act only after something breaks, but today’s attacks start long before any alert is triggered. Th
Jan 16, 2026 · 9 min read
Why Third-Party Ecosystems Create One of the Biggest Cyber Risks
Most organizations track their own systems well, servers, cloud apps, endpoints, and internal vulnerabilities. However, some of the highest-impact threats today don’t come from inside your network. They come from the sys
Jan 7, 2026 · 10 min read
What Executives and Boards Actually Expect From Digital Risk Protection
Executives and boards look at digital risk as a business risk. When executives ask about digital risk protection, they are not asking how many alerts were triggered or how many domains were monitored. They want to unders
Dec 18, 2025 · 9 min read
Identity and the New Attack Surface: Why Attackers Now Target People and Brands
Security teams spend years building defences around the systems they own, inside the organization. However, attackers changed direction. They no longer need to breach your network to harm you or your business. They now t
Dec 16, 2025 · 7 min read
Inside the Billion-Dollar Scam Mills: How Global Fraud Groups Are Industrializing Cybercrime
Most companies think of cybercrime as a set of isolated threats. However, that view is outdated. Online fraud is no longer a collection of small, disconnected attacks. It is a global industry run like a factory, with tea
Dec 11, 2025 · 6 min read
Why Impersonation Attacks Spread Faster Than Security Teams Can Detect Them
Modern impersonation attacks spread across domains, ads, social platforms, and news sites before internal tools see anything. By the time a team becomes aware, thousands of people may have already seen or interacted with
Dec 9, 2025 · 5 min read
Newsroom
Latest from Styx
Company announcements, product releases, and milestones.