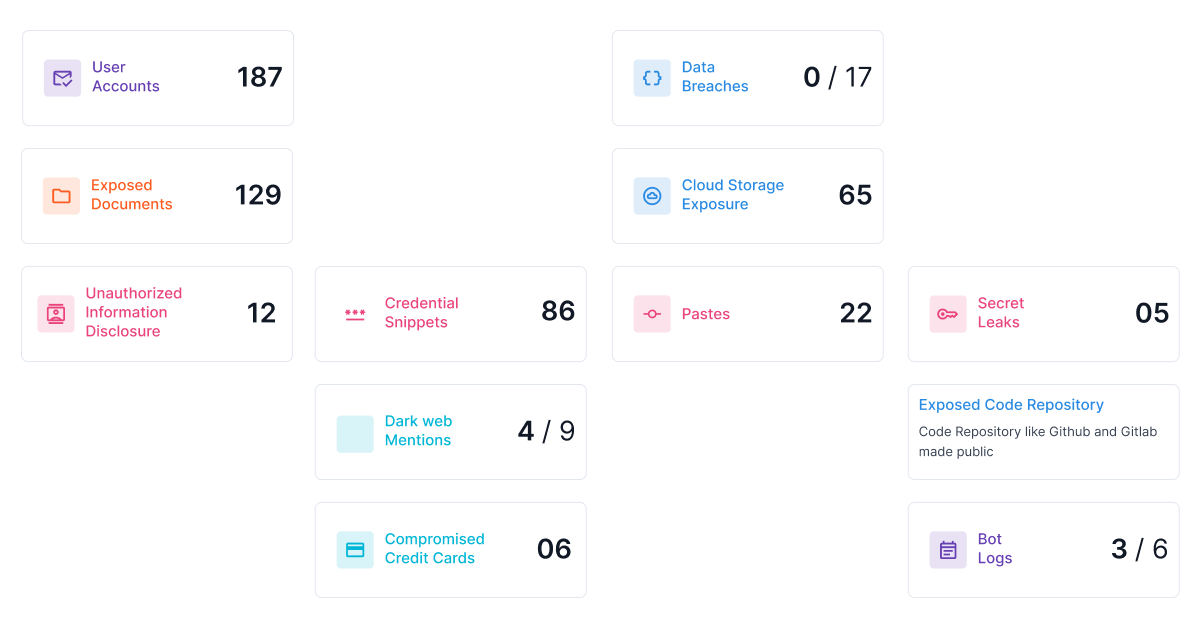
Dark Web and Credential Exposure
Data Leakage: What to Know and How to Prepare for Breaches
Styx Team · · 3 min read
Updated
Summarize this article with:ChatGPTGeminiPerplexityClaudeGrok
Phishing sites found, filed, and taken down by Styx
Book a demoRelated articles
Shadow IT Data Leakage: How Unapproved Tools Expose Data
Why Is Shadow IT a Data Leakage Problem? Most teams do not find shadow IT through a planned audit. They find it after company data appears in a tool, account, or folder that security never approved. That might be a custo
May 29, 2026 · 11 min read
How Account Takeover Attacks Work
Account takeover (ATO) attacks often start with access that looks legitimate. An attacker uses a stolen password, a leaked session token, a phishing link, or a fake login page to get into a real account. Once inside, the
May 8, 2026 · 7 min read
What Is Credential Stuffing?
Credential stuffing is when attackers use stolen usernames and passwords to break into accounts. They do not guess passwords. They use login details that have already leaked from past breaches, then test them across webs
May 2, 2026 · 7 min read